


Wondering whether the California Consumer Privacy Act (CCPA) actually applies to your WordPress site? For most small websites, the honest answer is probably not. But the law’s definition of ‘sharing’ personal information is wide enough to cover a Google Analytics tag or a Facebook Pixel, and California is not the only state writing rules like this.
We have worked through this on our own websites, so I know which parts of the CCPA touch a typical WordPress site and which parts you can safely set aside.
In this guide, I’ll show you how to ensure CCPA compliance for WordPress sites.
⚠️ We are not lawyers, and nothing on this website should be considered legal advice.
The quick answer – The CCPA applies to your for-profit business if it meets any one of these three tests:
- Your business generates more than $26,625,000 in annual gross revenue.
- You buy, sell, or share the personal information of 100,000 or more California residents or households per year.
- You earn 50% or more of your annual revenue from selling or sharing California residents’ personal data.
If that applies to you, staying compliant comes down to five main tasks:
- Audit what you collect – Perform a data audit covering every plugin and script on your site.
- Disclose what you do with it – Publish a privacy policy that clearly outlines the data you collect, why you collect it, and the visitor’s rights.
- Ask before you track – Add a cookie banner that blocks third-party scripts until users explicitly opt in.
- Record every consent choice – Keep a consent log so you can prove compliance if you’re ever audited.
- Answer requests quickly – Handle access, correction, and deletion requests with a form and WordPress’s built-in tools.
What is the California Consumer Privacy Act (CCPA)?
The California Consumer Privacy Act (CCPA) gives California residents direct control over how companies collect, store, and share their personal information. Its definition of ‘personal information’ is broad, covering names, email addresses, browsing history, and even biometric data.
Just like the General Data Protection Regulation (GDPR), the CCPA doesn’t only affect businesses based in California. If you handle data about people living there, then it may apply to you wherever your WordPress website is based.
The word that trips people up is ‘share’. You may never sell anyone’s data, but if your site runs display ads, a Facebook Pixel, or Google Analytics with advertising features switched on, you are sharing personal information for targeted advertising, and the CCPA treats that the same way as a sale.
Even below those thresholds, following these practices builds trust and prepares you for the other state privacy laws that may already apply to you.
Why Should WordPress Users Care About CCPA Compliance?
Ignoring the CCPA can get expensive. California’s privacy regulator can fine you up to $2500+ per violation, and up to $8,000 for each intentional violation or any violation involving someone you know to be under 16.
Consumers can also sue you directly if a breach happens because your security was inadequate.
Giving visitors real control over their personal information also builds trust with your audience.
How CCPA Affects Your WordPress Site
The CCPA gives visitors to your WordPress blog or website six rights: to know what personal data you hold about them, to delete it, to correct it, to opt out of its sale or sharing, to limit how you use sensitive information, and to exercise any of these without being charged more or given a worse service.
The steps below show you how to support each one.
CIPA and CCPA – How It Affects Small Websites
On January 1, 2026, new CCPA regulations added rules on automated decision-making technology, risk assessments, and annual cybersecurity audits. While they target large businesses and activities a typical site never performs, there is one development that does affect small sites.
Plaintiffs’ lawyers have been using the California Invasion of Privacy Act (CIPA), a wiretapping law from the 1960s, to sue websites over ordinary session recording, live chat, and advertising scripts, with statutory damages of $5,000 per violation.
According to a July 2026 analysis from the law firm Spencer Fane, these claims grew from roughly 600 filings to more than 4,000 and now make up around two-thirds of active California privacy litigation.
CIPA sets no revenue threshold at all, so a small site running analytics and a chat widget is exposed in a way the CCPA’s thresholds would never suggest. Courts are still divided on whether these old statutes apply to modern web tracking, but the practical fix is to find out which cookies your site sets, then get consent before those scripts load.
How to Improve Your CCPA Compliance in WordPress
You can click the links below to jump ahead to any section:
- Perform a Data Audit
- Create a Privacy Policy
- Add a Cookie Popup
- Write a Separate Cookie Policy
- Block Third-Party Scripts
- Track and Log Visitor Consent
- Build Trust with Opt-Outs
- Support the ‘Right to Correct’
- Support the ‘Right to Delete’
- Handle Data Access Requests Efficiently
- Secure Your WordPress Site
- Review Third-Party Contracts
- WordPress and CCPA Compliance: FAQs
- Additional Privacy Regulation Resources
Perform a Data Audit
The first step is to identify and document every type of personal data you collect, process, and store. To start, I recommend listing all the WordPress plugins and tools that gather data on your site, such as analytics plugins, form builders, and SEO plugins.
For example, if you’ve created a quote request form, then your form builder plugin might collect the visitor’s name, company name, and job title. For each tool, ask yourself these questions:
- What specific personal data does it collect? This might be names, email addresses, IP addresses, or payment details.
- Where is this data stored? Is it on your own server, or sent to a third-party service?
- Why is this data being collected? Is it essential or non-essential, and how are you using it?
- How long is this data kept? Do you have a retention policy for it?
- Is this data shared with anyone? In particular, are any service providers or advertisers involved?
I recommend recording the answers in a simple spreadsheet, so you have a documented overview to reference whenever your privacy practices change.
While you have that list in front of you, look for anything you can simply stop collecting. Every form field and tracking script you remove is data you never have to protect, disclose, or delete later.
Create a Privacy Policy
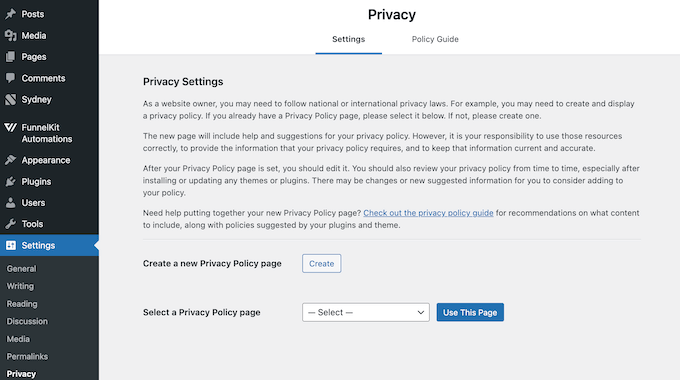
A privacy policy explains what personal data you collect, why you collect it, and who you share it with.
WordPress comes with a built-in generator for this, which you’ll find at Settings » Privacy in your dashboard.
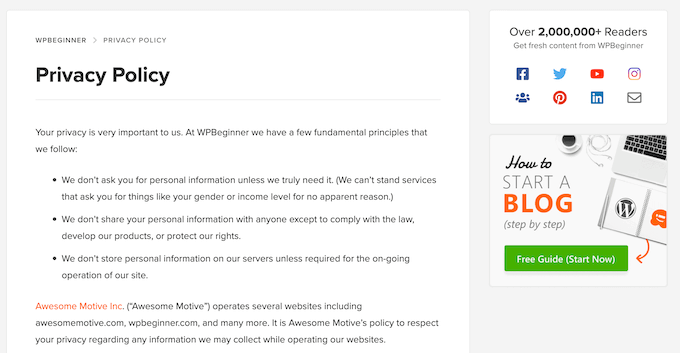
Alternatively, you can use our WPBeginner privacy policy as a starting point.
Just remember to replace every reference to WPBeginner with your own site name.
We also have a complete, step-by-step guide on how to add a privacy policy in WordPress.
Do you already have a privacy policy? Then update it to cover the six CCPA rights listed earlier, and tell visitors how to use them. For example, you could link to a contact form where they can ask for a copy of their data.
One newer requirement is easy to overlook.
You must list the categories of sensitive personal information you collect, such as account credentials or precise geolocation.
Finally, your privacy policy needs to be easy to find, so link it in your site’s header or footer to put it on every page. It’s also worth reviewing whenever your data handling practices change.
Add a Cookie Popup
The CCPA doesn’t always require visitors to opt in to data collection, but it does require that they can find out about it and opt out. A cookie popup does both, telling visitors what cookies you use and why, and giving them a straightforward way to decline.
There are many cookie banner plugins on the market, but I recommend WPConsent, a privacy compliance plugin built to meet many different privacy standards, including the CCPA.
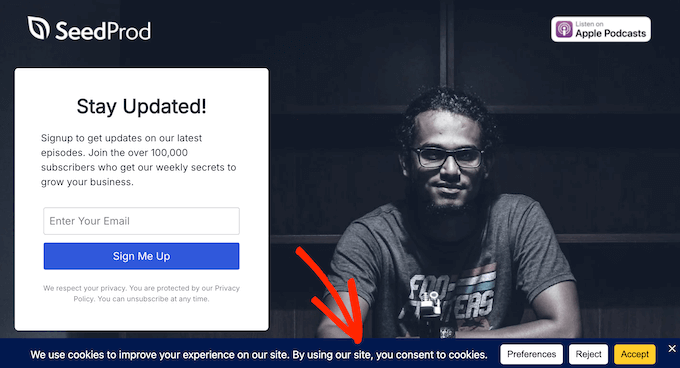
We use WPConsent to display cookie banners and manage user consent across our own websites.
The free WPConsent plugin comes with many essential features: the cookie banner, automatic script blocking, the site cookie scanner, a cookie policy generator, and support for Google Consent Mode v2.
The premium version of WPConsent adds consent logs, scheduled rescans, geolocation rules, automated translations, and a dedicated ‘Do Not Sell’ page. The consent logs and Do Not Sell page are the two that matter specifically for CCPA compliance.
💡 Want to learn more about our direct experience with WPConsent? Check out our in-depth WPConsent review.
To get started, install and activate the plugin, as normal. Upon activation, WPConsent will scan your entire site for active cookies and record all the ones it finds.
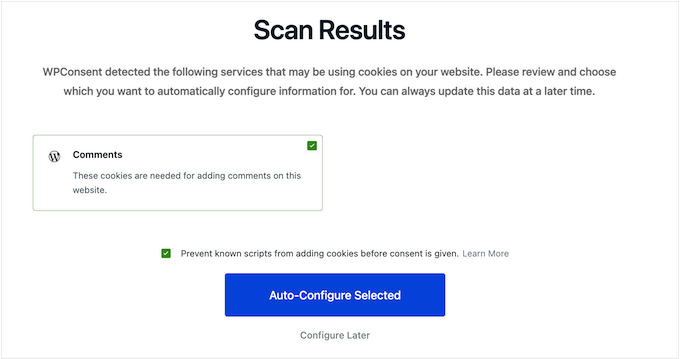
A setup wizard then walks you through customizing the popup.
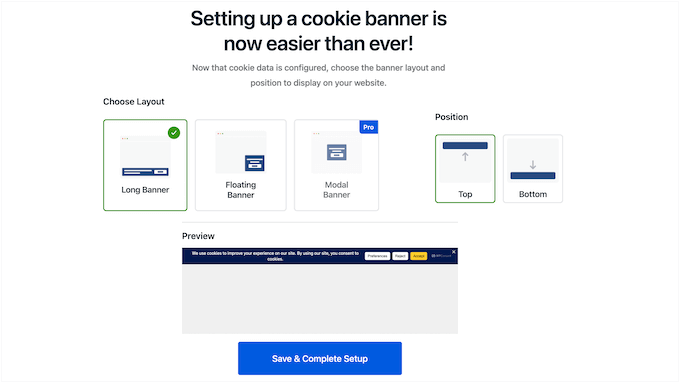
When you’re happy with the banner, save your changes and you’re done. For more details, see our guide on how to add a cookie popup in WordPress.
Write a Separate Cookie Policy
Alongside your banner, it’s a good idea to publish a cookie policy.
A good one lists the types of cookies you use, such as essential, analytics, or marketing, explains their purpose, such as tracking website visitors or delivering targeted ads, and says what personal information they collect, like IP addresses or browsing history.
You should also link to it from both your main privacy policy and your cookie banner, so visitors can find it easily.
Once again, WPConsent can handle this for you, using the same scan that found your active cookies. To set it up, go to WPConsent » Settings, open the Cookie Policy dropdown, and choose the page where you want the policy to appear.
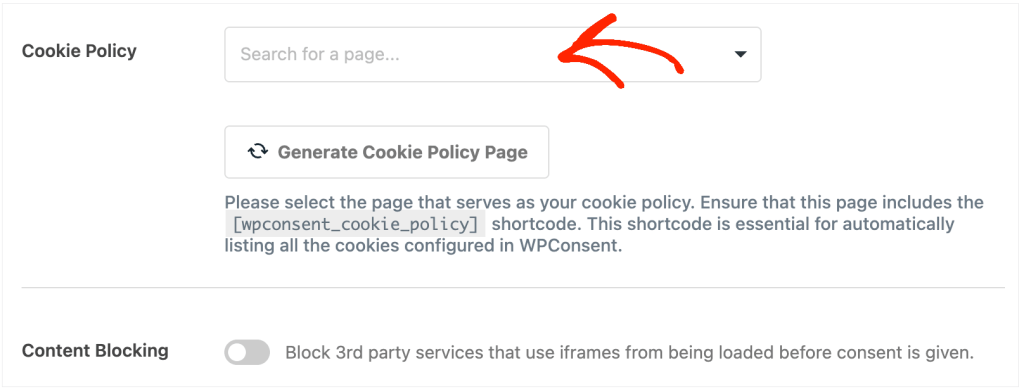
WPConsent then adds the policy to that page.
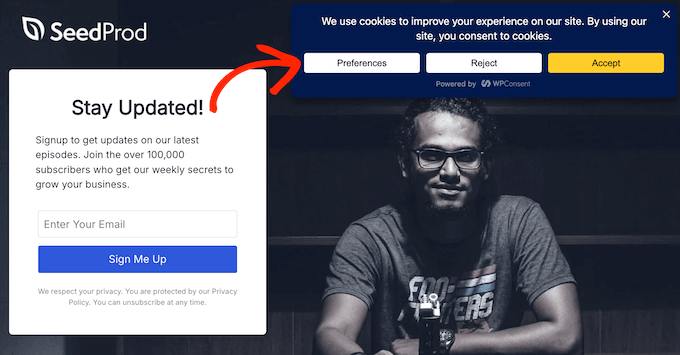
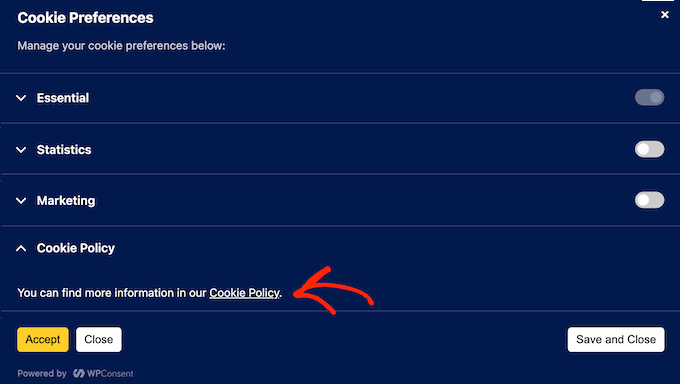
Visitors can reach the policy straight from your banner by clicking the ‘Preferences’ button.
From there, they select the ‘Cookie Policy’ link.
Block Third-Party Scripts
CCPA compliance also applies to the external tracking tools on your site, like Google Analytics and Facebook Pixel. Because these tracking tools collect data from your visitors, you are responsible for how they collect, store, and use it, and you need to let visitors opt out.
You can control these tools via automatic script blocking, which stops tracking scripts from loading until a visitor gives consent. That makes third-party tracking opt-in, which goes beyond what the CCPA requires.
However, once your trackers wait for consent, Google Analytics will only count the people who click ‘Accept’. This means your reported traffic will drop. Some visitors decline, and others never answer the banner.
WPConsent handles script blocking for you, and the feature is included in the free plugin. It recognizes common tracking scripts like Google Analytics, Google Ads, and Facebook Pixel, and holds them back so they cannot set cookies until a visitor gives permission.
To make sure this works on your site, go to WPConsent » Settings, find the Script Blocking toggle, and switch it on.
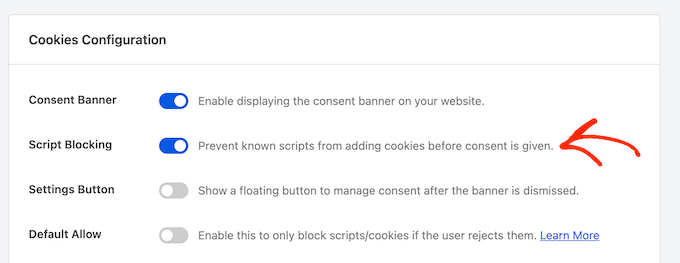
Then click ‘Save Changes’.
To check that it worked, open your site in a private browsing window and view the page source, which is the raw HTML your browser received. A tracker that WPConsent is holding back appears with ‘type=text/plain’ instead of a live address.
If you use a caching plugin, then clear your WordPress cache after enabling this setting, or the blocking won’t work for your visitors.
California law also requires sites to respect Universal Opt-Out Mechanisms (UOOMs), which are browser or extension signals that broadcast a user’s privacy choices across every website they visit. The main one is Global Privacy Control (GPC), sent automatically by browsers like Brave and extensions such as DuckDuckGo.
California’s first CCPA enforcement action was a $1.2 million settlement with Sephora, specifically because the company failed to process GPC signals.
WPConsent can detect and respect these signals, but it is switched off by default. Go to WPConsent » Settings and select the ‘Advanced’ tab.
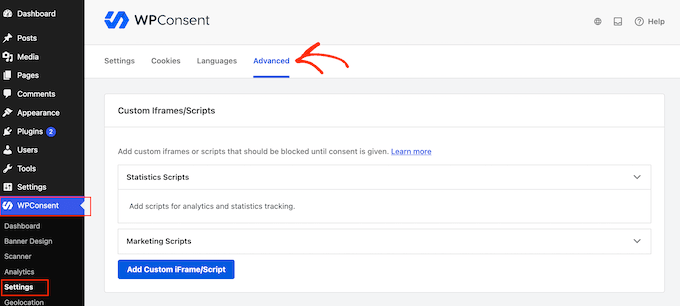
After that, enable the ‘Respect Global Privacy Controls’ slider and click ‘Save Changes.’
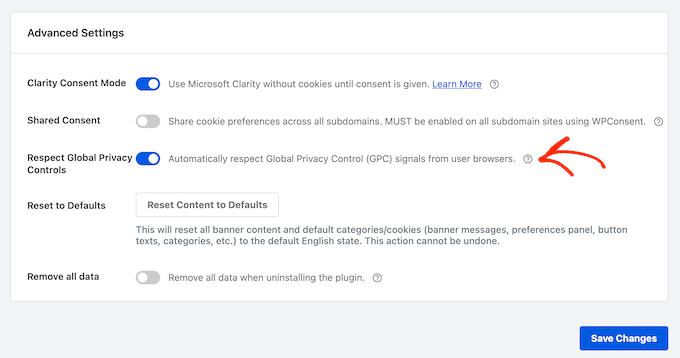
WPConsent now turns off non-essential cookies for visitors sending a GPC signal, so they won’t see your banner at all. It also shows them the confirmation message the 2026 rules require.
Track and Log Visitor Consent
If your data handling is ever questioned, or regulators audit you, you’ll need to prove that you respected your visitors’ choices. A consent log is that proof.
WPConsent Pro records this for you, capturing each visitor’s anonymized IP address, their consent choices, and the date and time those choices were registered.
Consent logging is switched off until you enable it, so first go to WPConsent » Settings » Consent Logs and turn it on. You’ll then find the records at WPConsent » Consent Logs in your dashboard.
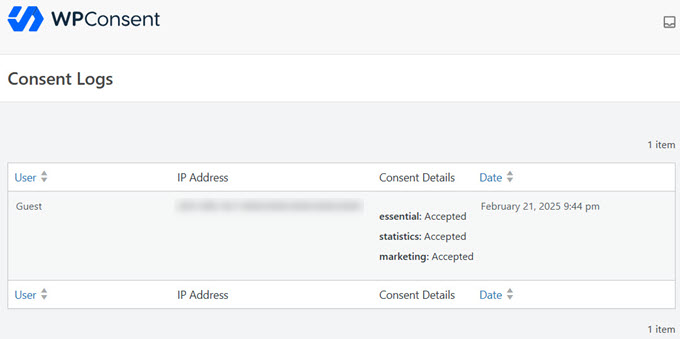
If you need to share them with an auditor, you can export the log directly from your dashboard.
Build Trust with Opt-Outs
The CCPA requires a clear ‘Do Not Sell or Share My Personal Information’ link on your homepage and every page where you collect personal information, which is why it normally lives in the footer and points to a dedicated opt-out page.
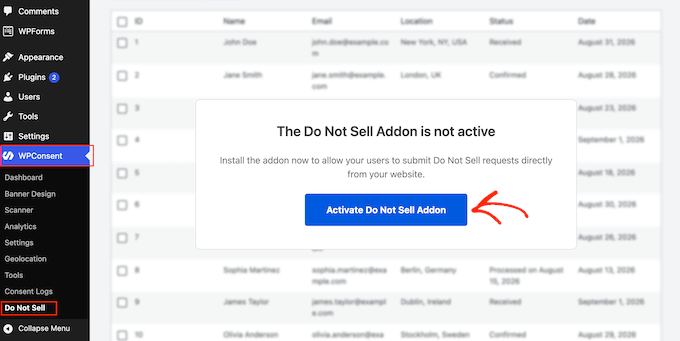
The easiest way to handle this in WordPress is WPConsent’s Do Not Sell addon, which can place a ready-made request form on any page. The addon is included in the Plus plan and above.
To install it, go to WPConsent » Do Not Sell and click the install button.
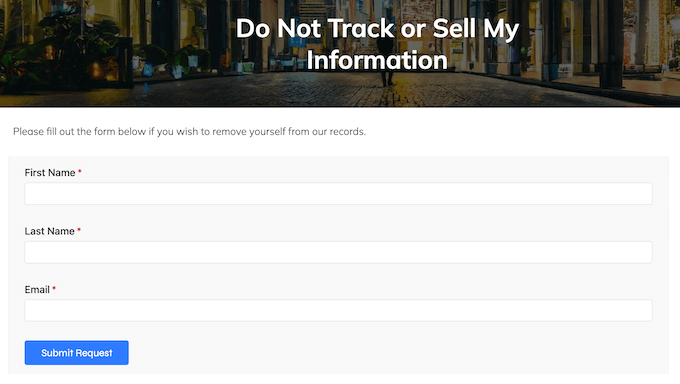
Next, go to WPConsent » Do Not Sell, select the ‘Configuration’ tab, and click ‘Generate Do Not Sell Page’. WPConsent creates the page with the opt-out form already on it. If you would rather use a page you have already published, choose it from the ‘Do Not Sell Page’ dropdown instead.
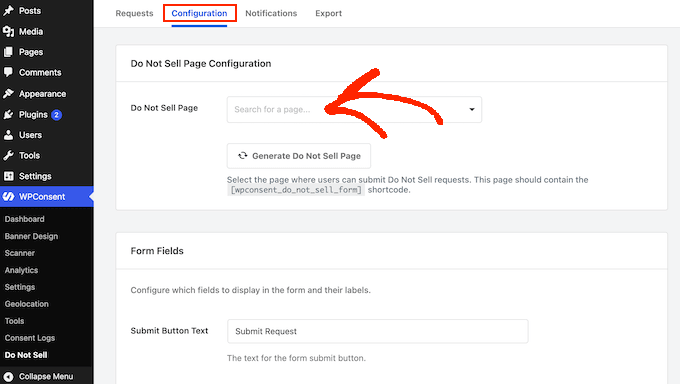
You can now choose what information the form asks for. Keep it to the name and email fields that are already on, because an opt-out is not a request you have to verify, and extra fields only add friction.
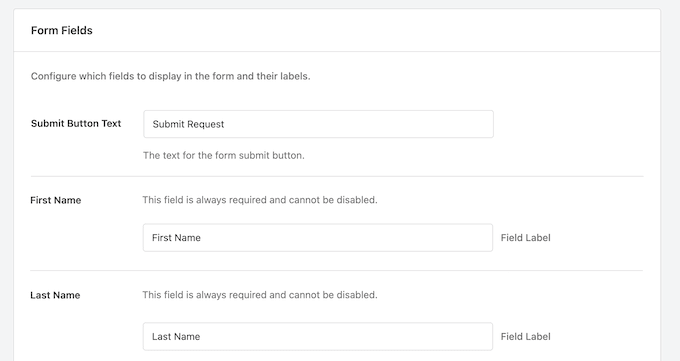
Finally, add a link to this page in your footer menu so it appears on every page. Visitors can then use it to opt out of the sale or sharing of their personal data. For a more detailed walkthrough, see our guide on how to create a Do Not Sell My Info page in WordPress.
WPConsent logs every request with names, email addresses, timestamps, and status, and stores them on your own site. Each request is a to-do rather than a switch: remove that person from any ad audiences or customer lists you upload to ad platforms, then mark the request as processed.
Support the ‘Right to Correct’
Consumers can ask you to correct any inaccurate personal information you hold about them. The simplest way to support this is a data correction request form.
WPForms is perfect for this, as its Personal Information Form template includes an ‘Update Existing Record’ checkbox to help you identify correction requests.

This template is included in every paid WPForms plan, starting with Basic.
It covers legal name, nickname, email address, and phone number, and you can add more fields in the drag-and-drop editor.

When a correction request arrives, verify the requester’s identity before you update your records. It’s also worth logging each request and the action you took, which serves as proof of compliance if you’re ever audited.
Support the ‘Right to Delete’
Users can also request that you delete their personal data. I recommend handling this with a deletion form built with a plugin like WPForms, which has a dedicated GDPR Right to Erasure Request Form template. That template is part of WPForms Pro and higher.
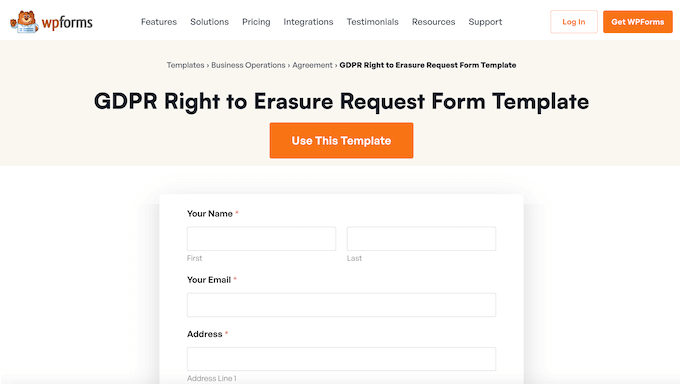
🌟 Want to learn more about this powerful form builder plugin? Check out our detailed WPForms review.
Once the form is live, link to it from your privacy policy page or embed it directly, so visitors can find it.
WPForms also has a built-in entry management system, so you can filter submissions across your forms and spot deletion requests quickly.
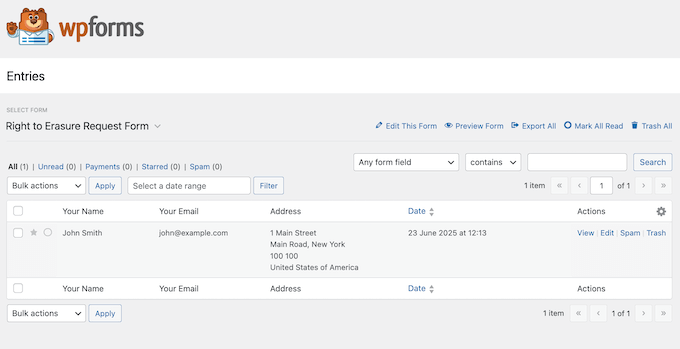
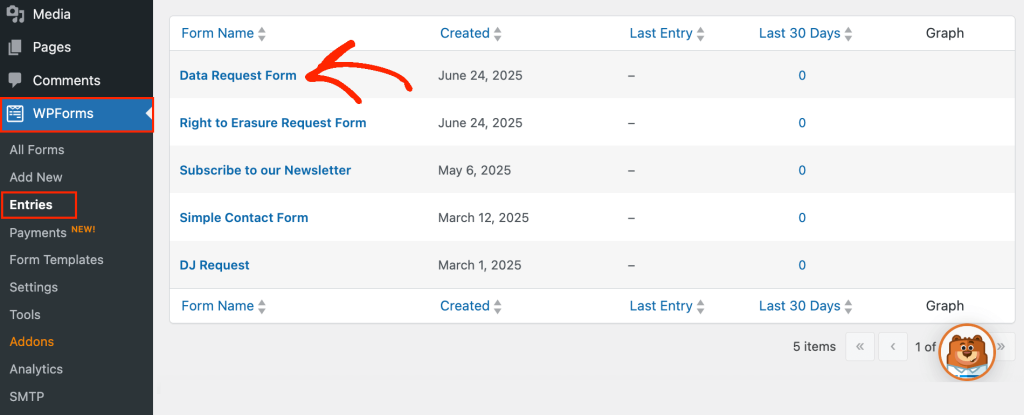
To review your entries, head to WPForms » Entries, where you’ll see every form on your website.

Find your data erasure form and click it to see all your ‘delete data’ requests.
Always verify the user’s identity before deleting their information, as this action is permanent and cannot be undone.
Once verified, head over to Tools » Erase Personal Data.
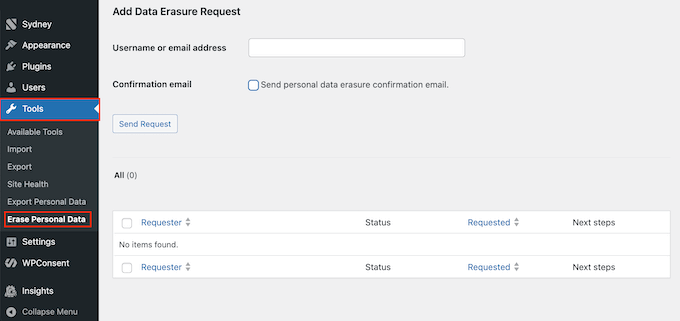
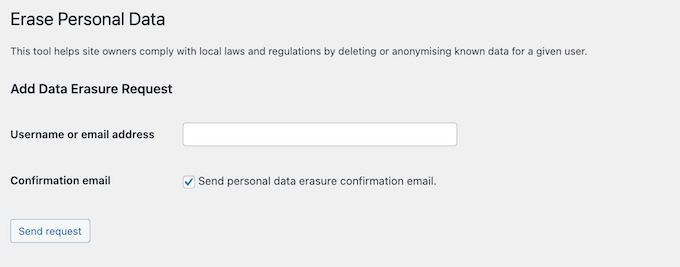
In the ‘Username or email address’ field, type in the details of the user you want to remove. The tool also has a ‘Send personal data erasure confirmation email’ setting, which tells the user when you’ve finished.
Handle Data Access Requests Efficiently
Under the Right to Know, consumers can request a complete report of the personal information you have collected, stored, or shared about them.
Since January 1, 2026, this is no longer capped at a rolling 12-month window, so if you keep customer data for longer than a year, you must reach back as far as January 1, 2022.
WPForms offers a ready-made Data Request Form template for this, which is part of WPForms Pro and higher.
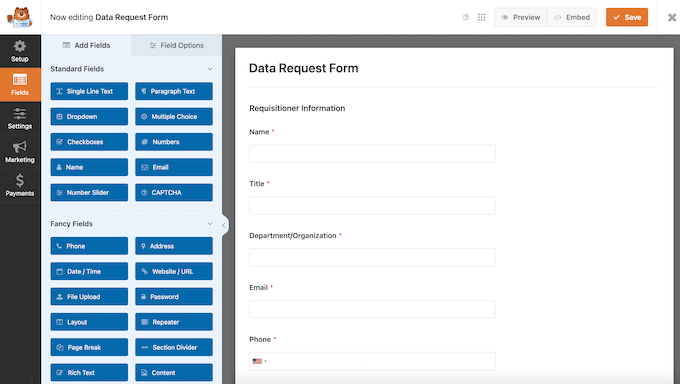
After adding this form to your site, go to WPForms » Entries and select it to see the requests as they come in.
To answer one, export that person’s information as a .zip file by going to Tools » Export Personal Data.
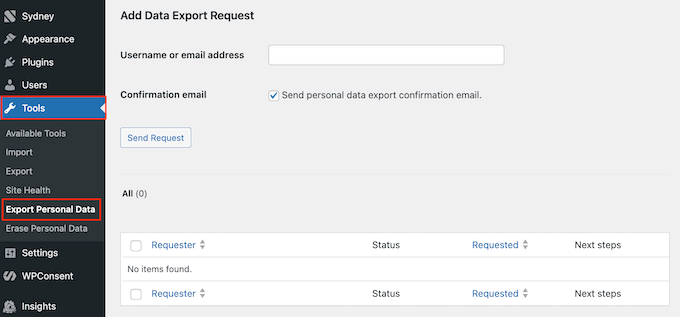
Enter the user’s email address or username, click Send Request, and then share the .zip file with the person who asked for it.
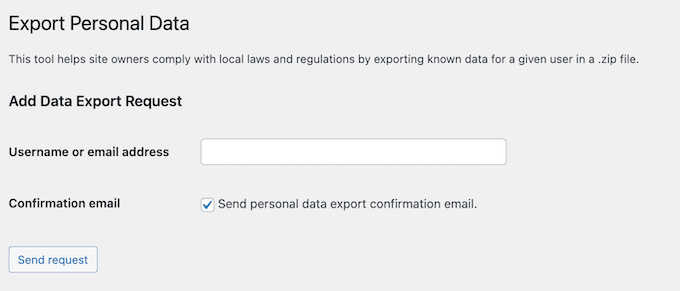
For a closer look at both built-in tools, see our guide on how to export and erase personal data in WordPress.
Secure Your WordPress Site
The CCPA lets consumers sue you for a breach caused by a failure to implement reasonable security measures, at $107 to $799 per consumer, per incident. That makes securing your site a legal requirement, not just good practice.
With that in mind, make sure you have the basics covered: a security plugin, regular updates, strong passwords with two-factor authentication, reliable hosting, backups, and spam protection on your forms. Our ultimate WordPress security guide covers each one step by step.
- Install a security plugin to protect your site from malware, brute force attacks, and other common threats.
- Keep WordPress core, plugins, and themes updated, because outdated software is one of the most common causes of security vulnerabilities.
- Use strong, unique passwords for all admin accounts, and enable two-factor authentication wherever possible.
- Choose a reliable WordPress hosting provider that offers SSL certificates, firewalls, and server-level security updates.
- Set up regular WordPress backups so you can recover quickly after a breach or data loss.
- Add anti-spam protection like CAPTCHA to your forms to prevent automated attacks and spam submissions.
Together, these steps are what ‘reasonable security measures’ means in practice.
Review Third-Party Contracts
If you share personal data with third-party services, such as email marketing services, analytics tools, payment processors, or advertising networks, then the CCPA requires a contract that limits what they can do with it. In practice, the major providers build this into their standard terms, so check that each vendor’s terms or data processing agreement covers California, and note it in your audit spreadsheet.
WordPress and CCPA Compliance: FAQs
Is GDPR more strict than CCPA?
Generally yes, the GDPR is stricter. The biggest practical difference is consent, as the GDPR requires visitors to opt in before you set non-essential cookies, while the CCPA mostly works on an opt-out basis.
The GDPR also applies to any organization handling EU residents’ data, no matter how small, while the CCPA only applies once you hit specific thresholds. That means a small blog can be exempt from the CCPA while still fully bound by the GDPR.
For the full walkthrough, see our ultimate guide to WordPress and GDPR compliance.
My site is under the CCPA thresholds. Do other state privacy laws apply to me?
Quite possibly, because every state sets its own thresholds. Around 20 states now have comprehensive consumer privacy laws in effect, and several of them cover businesses the CCPA wouldn’t apply to.
Fortunately, you don’t need a separate strategy for each one, as a privacy policy, a script-blocking banner, a data request system, and a consent log will help you meet privacy laws in multiple states.
For the state-specific details, see our guides to VCDPA compliance in WordPress and UCPA compliance in WordPress, or our guide to WordPress privacy compliance for the shared rules.
How often should I review my CCPA compliance?
Every website is different, but I recommend reviewing at least once per year, and every time you make big changes to how you handle user data. Since the fine thresholds adjust for inflation every odd-numbered year, double-check any specific figures in your documentation in 2027.
Additional Privacy Regulation Resources
These resources will help you keep up with evolving privacy regulations and best practices:
- The Ultimate Guide to WordPress Privacy Compliance
- How to Know if Your WordPress Website Uses Cookies
- How to Create a Do Not Sell My Info Page in WordPress
- The Ultimate WordPress Security Guide – Step by Step
I hope this ultimate guide to WordPress CCPA compliance has helped you understand this important privacy law. Next, you may want to see our expert picks for the best WordPress security plugins or the best analytics solutions for WordPress users.
If you liked this article, then please subscribe to our YouTube Channel for WordPress video tutorials. You can also find us on Twitter and Facebook.




vaibhav
thanks, it was very helpful
WPBeginner Support
Glad it was helpful!
Admin
mike
very thorough article.. saving for later when i hopefully meet the criteria!
WPBeginner Support
Glad you liked it and it will be here when you’re ready
Admin
Ashraful Haque Akash
Thank you for this important and detailed information.
WPBeginner Support
You’re welcome!
Admin
Kamran
Rhanks for the amazing and detailed post.. Was in search of this for a long time
WPBeginner Support
You’re welcome
Admin
Huzaifa Al Mesbah
Awesome guide on CCPA compliance for WordPress! Your clear, actionable steps make this complex topic so much easier to handle. Thanks for the practical tips on data audits and using WPConsent!
WPBeginner Support
You’re welcome, glad our guide was helpful!
Admin
Faisal Ahammad
Thanks for this clear and helpful guide! As a beginner, I found the step-by-step instructions and plugin recommendations really easy to follow. It makes CCPA compliance less confusing and more doable. Appreciate the practical tips!
WPBeginner Support
You’re welcome!
Admin
Okafor Franklyn Chukwuemeka
Data privacy is an essential in website development, as a beginner in WordPress, I learnt that the hard way. Thanks for this insight
WPBeginner Support
You’re welcome!
Admin
Arsalan
Great guide! The CCPA can be confusing, so having a clear, step-by-step breakdown for WordPress users is incredibly helpful.
WPBeginner Support
Glad you liked our guide!
Admin
Toine
Very nice! Thank you
WPBeginner Support
You’re welcome
Admin
AM
Thanks for a very informative article. I really appreciate that you put the CA requirements upfront. I’ll have to sell a LOT of books to make those thresholds.
WPBeginner Support
Glad we could share
Admin
Aiesha
Helpful as always, thank you!
WPBeginner Support
You’re welcome!
Admin
Kerri
Very helpful. Sounds like I don’t need to be concerned.
WPBeginner Support
Glad we could still bring it to your attention
Admin
Amandine
A great article and guide to managing CCPA and data in general.
I didn’t know you had to be CCPA compliant even if you’re not based in the USA. I’ll definitely get onto it.
Would love to get a post about how to manage multiple data privacy acts.
WPBeginner Support
We will look into the possibility in the future
Admin
April
Great info. here about CCPA compliance. Thank you for this!
WPBeginner Support
You’re welcome!
Admin
Matt
Doesn’t really apply to me but great article! You guys make great stuff.
WPBeginner Support
Glad you like our content, even if you are not required for your site, it includes helpful tools for your users
Admin
Amr Fawzy Amer
That guide is so helpful. Thanks for the great effort you put into this.
WPBeginner Support
You’re welcome, glad our guide was helpful!
Admin
Pierre Wouters
I have been following WP Beginner for many years, and always found something new, or a useful tutorial.
Thank you!
WPBeginner Support
You’re welcome
Admin
Nonofo Joel
This is an excellent post on CCPA compliance, as a WordPress user and getting traffic from California, its good insight for me to implement on website I have built.
WPBeginner Support
Glad you found our article helpful
Admin
Aina Oluwatimilehin
WPbeginner has been my go to site for resources on WP.
Thank you.
WPBeginner Support
You’re welcome
Admin
Sridhar Paruchuri
Wow, this is exactly the kind of resource I’ve been looking for! The step-by‑step breakdown from data audits to handling deletion and access requests makes CCPA compliance feel completely manageable. I especially appreciate how you walked through using WPConsent for cookie management and WPForms for user data requests. It takes what seems like a legal headache and turns it into actionable WordPress steps. Thanks for making privacy compliance so approachable and practical for non-lawyers like me.
WPBeginner Support
You’re welcome, glad our guide can be helpful
Admin
Christian Morris
What an informative post
WPBeginner Support
Glad you think so
Admin
Vidya Sury
Thanks for breaking it all down so clearly. Consent is a confusing topic right now and it is hard to figure out what we need to do to stay on the right side.
WPBeginner Support
You’re welcome!
Admin
Syed Sazzadul Bari
This was a genuinely helpful and timely guide—thank you for breaking down such a complex topic in a beginner-friendly way. As privacy laws become stricter, it’s easy for small website owners to feel overwhelmed. Your step-by-step approach and mention of tools like WPConsent provide real, actionable value. Especially appreciated the emphasis on building trust, not just avoiding fines—something we often overlook in compliance discussions. Great work!
WPBeginner Support
You’re welcome!
Admin
Abid Hasan
Great article, thank you for the insights.
WPBeginner Support
You’re welcome!
Admin
Foysal
Thanks for sharing this beginner-friendly guide.
WPBeginner Support
You’re welcome!
Admin
Gopal K
very helpfull for bloggers
WPBeginner Support
Glad you think so
Admin
Helen Putre
Thanks for the deep dive into privacy compliance and how to enhance it on my site.
WPBeginner Support
You’re welcome!
Admin
Caron
Thank you for such an in-depth article, fantastic!
WPBeginner Support
You’re welcome!
Admin
Bruce Spedding
I’m never sure if I’m obliged to follow this – based in New Zealand
WPBeginner Support
Even if not required for your site, there are helpful tools for users to have in these recommendations
Admin
Stuart Hasson
WP Beginner has been SO helpful in giving me insights and updates to help make my website more useful and productive.
WPBeginner Support
Glad our guides have been helpful
Admin
David
Cool. pieces. Read you almost every morning!
WPBeginner Support
Glad we can be your morning reading
Admin
Reza
Lots of things I didn’t know here, thanks.
WPBeginner Support
Glad we could share
Admin
Sieglinde Anderson
I have used WPBeginner tutorials for over 10 years. I received such helpful information not only for my blog but also for my website. I collected most of them in a file but sadly Hurricane Helene destroyed my internet for over 3 months and Microsoft removed all saved files where they cannot be found.
I know the information I need is on WPBeginner’s site and I feel very grateful that I can access and get what I need to learn. Thank you for your generosity and all the information you provide free.
WPBeginner Support
Glad we can continue to offer our tutorials for you!
Admin
Robert Tillotson
Wow a lot of stuff here. too long to read and digest in one sitting.
WPBeginner Support
You can always come back and go over part of the article instead of everything at once
Admin
Carolyn Dean
Thank you for this important and detailed information.
WPBeginner Support
You’re welcome!
Admin
Lisa Angle
Thank you for all you do to help people learn WordPress!
WPBeginner Support
Glad we can be helpful
Admin
René Joergensen
Thanks for sharing about CCPA, and how to avoid breaching and risk a fee.
WPBeginner Support
You’re welcome
Admin
Daphane
I appreciate all the education you provide about Wordpress and spotlight news
WPBeginner Support
Glad to hear you find our content helpful
Admin
Paul Sahota
Excellent breakdown of CCPA requirements for WordPress users. The section on data handling and plugin recommendations stood out, especially the WPForms integration for data access requests.
I would love to see a future post comparing the CCPA with GDPR for multi-region site owners.
WPBeginner Support
We will look into the possibility
Admin
Dayo
I’ve not really given the privacy and compliance ethics a thought, maybe became I’m in Africa where such laws are not highly enforced. I’ll ensure to take that seriously from today, beginning with the WPConsent plug-in.
Thank you.
WPBeginner Support
Glad we could share this with you
Admin
Jesse Mwangi
This guide is incredibly helpful — especially for developers and site owners working with clients in or targeting California. The breakdown of what CCPA is, how it differs from GDPR, and how to make your WordPress site compliant is very clear and actionable.
Thank you WPBeginner for always making complex topics easier to understand and implement. I’ll definitely be referencing this in future projects!
WPBeginner Support
You’re welcome, glad you found the guide helpful!
Admin
Olena
Thanks for such an interesting and helpful post!
WPBeginner Support
Glad you found it helpful!
Admin
Samuel Ipinlaiye
Amazing. Very insightful article.
WPBeginner Support
Glad you think so
Admin
Md Moniruzzaman Monir
Thank you for your detailed answer.
WPBeginner Support
You’re welcome
Admin